Why the Mobile Access Standard Is Critical to Building Operations
For decades, facility managers and building operators have been trapped by proprietary lock-in in access control systems. The Aliro standard—the first interoperable, non-proprietary mobile credential standard launched by the Connectivity Standards Alliance in February 2026—allows a single credential to be used on authenticated readers from different manufacturers. Kastle became the first company to deploy Aliro-authenticated mobile credentials simultaneously in Apple Wallet, Google Wallet, and Samsung Wallet. This article explores the standard's practical impact on building operations and its path to adoption.
Author: Haniel Lynn, CEO of Kastle Systems International. The views expressed in this article are solely those of the author.
For decades, facility managers and building operators have been caught in the same cycle: procure an access control system that works well initially, but when upgrades are needed, tenants make new demands, or new properties are acquired, they find themselves firmly locked in—credentials cannot be used on readers from other manufacturers, and software cannot interoperate with other systems. The only way out is a complete replacement of equipment, which few have the budget or willingness to do.

This is not a system flaw but a business model. Proprietary ecosystems create vendor lock-in, generating predictable revenue for manufacturers while causing recurring headaches for building managers. Mixed-use properties feel this most acutely: within a single building, office floors, retail tenants, parking garages, and amenities often run separate security systems—credentials are not universal, management is not unified, and only silos that consume time and money remain.
The industry has discussed solutions for years. With the launch of the first interoperable, non-proprietary mobile credential standard, we have taken a true first step.
The Aliro Standard: Breaking Down Proprietary Barriers
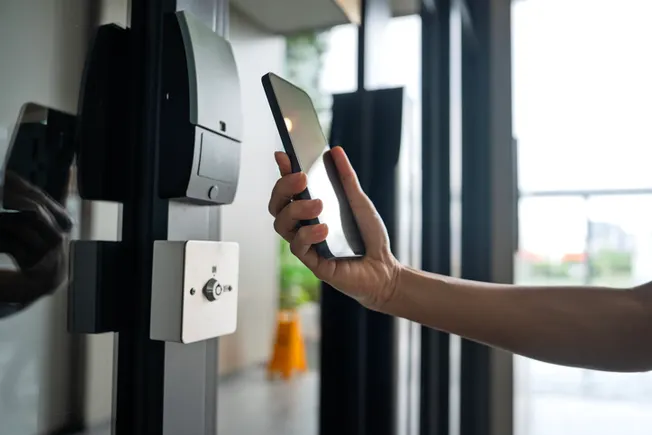
Aliro is the first interoperable, non-proprietary mobile credential standard, launched by the Connectivity Standards Alliance in February 2026. It establishes a protocol that enables a single credential to be used on certified readers from different manufacturers. At this year's International Security Conference and Exposition in Las Vegas, Kastle became the first company to deploy Aliro-certified mobile credentials simultaneously in Apple Wallet, Google Wallet, and Samsung Wallet.
Aliro achieves the following:
- Resolves credential-reader incompatibility issues.Mobile credentials can be used on any Aliro-certified reader, regardless of manufacturer. The identifier on the credential no longer needs to match the reader—a major change that breaks one of the most stubborn links in the proprietary access control model.
- Establishes a protocol between credentials and readers.This lays the foundation for future developments—including backend integration, system connectivity, and coordinated infrastructure built on the standard. It is a viable and practical starting point for multi-vendor environments in complex buildings.
Practical Impact on Building Operations
The practical impact of this first step is profound. Credential provisioning becomes simpler—no more dealing with cross-platform format compatibility issues or waiting for temporary solutions when tenants use different mobile ecosystems. Operational flexibility increases because upgrading or replacing readers is no longer constrained by a single vendor's technology roadmap. For mixed-use properties, achieving a common credential framework across different areas of the same building is also within reach.
For managed service providers like Kastle, Aliro also reinforces what we have been working toward for years: making multi-tenant, multi-system environments run smoothly in complex buildings. The standard makes credentials portable, and our job is to make the operations, integration, and day-to-day management around those credentials seamless for building managers.
Why Adoption Rates Matter
A standard's value depends on its adoption, and Aliro is no exception. Consider wallet payments: Apple Pay launched in 2014, but it took over a decade—until enough point-of-sale terminals were upgraded—for mobile payments to become the norm. The technology was ready; infrastructure lagged behind.
Aliro will follow a similar path. The more manufacturers deploy Aliro-certified readers, the greater the value of the credential. We are at the beginning of the curve. The standard has been validated and is practical. The question is how quickly the installed base of compatible hardware grows.
Facility managers and building operators can play a role. When evaluating access control vendors, specifying systems for new projects, or negotiating upgrades, ask whether they support Aliro. The speed of adoption depends in part on how loud the market demand is.
The Road Ahead
As buildings compete for tenants and companies compete for talent, offering simple, platform-agnostic mobile access is becoming a baseline expectation. Interoperability is not an add-on feature but an operational requirement. Facility managers who push vendors to adopt standards like Aliro will spend less time managing incompatible systems and more time on what truly matters: security, tenant experience, and operational efficiency.
We are at the beginning of this transformation. Aliro does not solve every problem, but it proves that open, interoperable mobile access is feasible, practical, and secure. The industry has set the standard; now it is up to manufacturers, integrators, managed service providers, and the building professionals who specify and procure these systems to make it the norm.